What is Kibana? A 2026 Guide to Elasticsearch Dashboards
Kibana is the open-source visualisation and exploration interface of the Elastic Stack. It lets you search, analyse and build dashboards from data stored in Elasticsearch, such as logs, metrics, security events and business data, without writing queries by hand.
Modern organisations generate vast amounts of operational, application, and security data every day. Collecting that information is only the first step. Turning it into actionable insights requires a platform capable of exploring, visualising, and monitoring data in real time.
This is where Kibana plays a central role. As the visualisation and analytics interface of the Elastic Stack, Kibana enables organisations to transform Elasticsearch data into interactive dashboards, reports, and monitoring tools that support faster decision-making.
Whether you're monitoring infrastructure, analysing application performance, investigating security events, or tracking business metrics, Kibana provides a flexible way to explore data and present it in a meaningful format.
This guide explains what Kibana is, how it works with Elasticsearch, how it compares with Elasticsearch and Grafana, how to get started, and how to build dashboards that deliver real business value. If you already know the basics, jump straight to our guide on building real-time dashboards with Elasticsearch and Kibana.
What is Kibana?
Kibana is the visualisation and analytics platform for Elasticsearch. It enables organisations to explore, analyse, and present data stored in Elasticsearch through interactive dashboards, charts, maps, and reports.
As part of the Elastic Stack, Kibana provides a user-friendly interface for searching data, monitoring system performance, analysing application logs, investigating security events, and tracking business metrics without requiring users to query Elasticsearch directly.
Rather than acting as a standalone business intelligence tool, Kibana is designed to work natively with Elasticsearch, allowing organisations to analyse large volumes of structured and unstructured data in near real time.
Its flexibility makes it suitable for a wide range of use cases, including observability, cybersecurity, IT operations, application monitoring, and business analytics.
How does Kibana work with Elasticsearch?
Elasticsearch and Kibana are designed to work together as complementary components of the Elastic Stack.
Elasticsearch collects, indexes, and stores data from multiple sources, while Kibana provides the interface used to search, visualise, and analyse that information. Together, they allow organisations to transform raw operational data into dashboards and insights that support faster decision-making.
This separation of responsibilities enables teams to process large volumes of data efficiently while presenting the results through intuitive visualisations tailored to different audiences.
A typical workflow follows these steps:
- Data is collected from applications, infrastructure, logs, metrics, or security tools.
- Elasticsearch indexes and stores the data for fast searching and analysis.
- Kibana connects to Elasticsearch to query the indexed data.
- Users create visualisations, dashboards, alerts, and reports based on that information.
- Teams monitor operations, investigate incidents, and share insights across the organisation.
Together, Elasticsearch and Kibana provide a unified platform for collecting, analysing, and visualising data, enabling organisations to move from raw information to actionable insights in near real time. By combining search, analytics, and visualisation within a single platform, teams can explore data, monitor operations, and share insights more efficiently across the organisation.
Related article: What is Elasticsearch and how does it work?
Kibana vs Elasticsearch: what is the difference?
Elasticsearch is the search and analytics engine: it stores, indexes and queries the data. Kibana is the interface on top of it: it lets people explore that data, build visualisations and dashboards, and manage the stack. Kibana cannot work without Elasticsearch, while Elasticsearch can be used without Kibana, for example through its API.
Kibana vs Grafana
Both tools build dashboards, but they are designed for different scenarios:
| Kibana | Grafana | |
|---|---|---|
| Data sources | Built for Elasticsearch | Many data sources (Prometheus, SQL, cloud services, Elasticsearch and more) |
| Best for | Log analysis, search, observability and security analytics | Infrastructure and metrics monitoring across several platforms |
| Integration | Deep integration with the Elastic Stack (Elastic Security, Observability) | Vendor-neutral, combines sources in a single dashboard |
If your data already lives in Elasticsearch, Kibana is the natural choice. If you need to combine metrics from several systems in a single view, Grafana is often a better fit, and many teams use both.
Why should organisations use Kibana?
Organisations generate vast amounts of operational data every day, from application logs and infrastructure metrics to security events and business transactions. Without the right tools, transforming that information into meaningful insights can be time-consuming and complex.
Kibana helps bridge this gap by providing a visual interface that enables teams to explore, analyse, and monitor Elasticsearch data in real time. Instead of relying on static reports or manually querying data, users can build interactive dashboards that support faster decision-making across the organisation.
Beyond data visualisation, Kibana enables organisations to improve operational visibility, investigate incidents more efficiently, and monitor key performance indicators through a single interface.
Improve operational visibility
Modern IT environments generate data continuously across applications, servers, cloud platforms, containers, and network infrastructure.
Kibana brings this information together in a single view, allowing operations teams to monitor system health, identify anomalies, and detect performance issues before they affect users.
Accelerate troubleshooting
Finding the root cause of an incident often requires analysing data from multiple systems.
By combining Elasticsearch's search capabilities with Kibana's visualisations, teams can quickly filter logs, identify patterns, correlate events, and investigate issues without manually reviewing large volumes of data.
This reduces the time required to diagnose problems and helps restore services more quickly.
Support security operations
Security teams can use Kibana to investigate authentication events, network activity, endpoint telemetry, and other security-related data stored in Elasticsearch.
Interactive dashboards make it easier to identify suspicious behaviour, analyse trends, and support incident response with greater visibility across the environment.
Enable data-driven decisions
Kibana is not limited to IT operations.
Business teams can also create dashboards that track operational KPIs, customer activity, service performance, or business metrics, helping decision-makers access relevant information in real time rather than waiting for manually generated reports.
Ultimately, Kibana enables organisations to move beyond simply collecting data and start using it to improve operational efficiency, strengthen security, and support better business decisions.
What can you build with Kibana?
One of Kibana's greatest strengths is its ability to support a wide range of business and operational use cases. By working directly with Elasticsearch, organisations can build dashboards tailored to different teams, processes, and decision-making needs.
Some of the most common use cases include:
Infrastructure monitoring
Track server health, CPU and memory usage, storage utilisation, network activity, and cloud infrastructure performance through real-time dashboards.
Application observability
Monitor application performance, analyse logs, identify errors, and understand how services behave across distributed environments.
Security monitoring
Visualise authentication events, firewall activity, endpoint telemetry, SIEM data, and threat detection dashboards to support security operations.
Business analytics
Build dashboards that consolidate sales data, operational KPIs, customer behaviour, or business metrics, allowing decision-makers to monitor performance through a single interface.
Log analysis
Explore logs generated by applications, operating systems, containers, and cloud services to investigate incidents, identify trends, and improve troubleshooting.
Rather than creating separate reporting tools for each department, organisations can use Kibana to deliver role-based dashboards tailored to different audiences while working from the same Elasticsearch data. This creates a single source of truth that improves collaboration, operational visibility, and decision-making across the organisation.
Related article: Building Real-Time Dashboards with Elasticsearch and Kibana
Getting started with Elasticsearch and Kibana
The quickest way to see Kibana in action is to run it against sample data:
- Run Elasticsearch and Kibana. Use Elastic Cloud, Docker or the official packages. Keep both components on compatible versions.
- Open Kibana in your browser. By default it is available on port 5601. On a first local setup, Kibana asks for the enrolment token generated by Elasticsearch to connect the two.
- Load sample data. From the Kibana home page, add one of the sample data sets to get ready-made dashboards to explore.
- Create a data view. A data view tells Kibana which Elasticsearch indices to query and which field holds the timestamp.
- Explore your data in Discover. Search, filter and inspect documents before building any chart.
- Build your first visualisation and dashboard. Create charts with Lens and combine them in a dashboard, as described in the next section.
To ingest your own logs and metrics, see our guide on how to integrate Elasticsearch, Logstash and Kibana.
How to build your first Kibana dashboard
Building an effective dashboard is not only about creating charts. The objective is to present the right information to the right audience, enabling faster and more informed decisions.
A structured approach helps ensure dashboards remain useful as data volumes and business requirements evolve.
1. Connect your data
Start by connecting Kibana to the Elasticsearch indices that contain the data you want to analyse. This may include logs, metrics, business data, application events, or security information.
2. Prepare your data
Well-structured data produces better dashboards. Review field mappings, timestamps, labels, and data quality before creating visualisations to ensure the information is accurate and consistent.
3. Create visualisations
Select the charts that best represent your data. Depending on the use case, this may include bar charts, line graphs, pie charts, tables, maps, or time-series visualisations.
4. Build interactive dashboards
Combine multiple visualisations into dashboards that provide a complete view of system performance or business activity. Filters and drill-down capabilities allow users to explore information in greater detail.
5. Configure alerts
Integrate Kibana with alerting capabilities to notify teams when predefined thresholds or conditions are met, enabling faster responses to operational or security events.
6. Share insights
Dashboards become more valuable when they support collaboration. Share dashboards across teams, generate reports, and ensure stakeholders have access to the information they need to make informed decisions.
A successful dashboard should simplify complex information, highlight the metrics that matter most, and enable users to identify trends or issues at a glance.
Best practices for Kibana dashboards
Building a dashboard is only the first step. To deliver long-term value, dashboards should be designed around the needs of their users, present reliable data, and remain easy to maintain as business requirements evolve.
Following a few best practices can help organisations maximise the value of Kibana while ensuring dashboards continue to support effective decision-making.
Focus on business outcomes
Dashboards should answer specific business or operational questions rather than display as much information as possible.
Whether the objective is monitoring infrastructure, tracking application performance, or analysing business KPIs, every visualisation should support a clear decision or action.
Keep dashboards simple
Overloaded dashboards make it harder to identify what matters.
Using a limited number of relevant visualisations, clear labels, and logical layouts helps users interpret information more quickly and reduces cognitive overload.
Ensure data quality
Even the best-designed dashboard is only as reliable as the data behind it.
Regularly reviewing data sources, index mappings, timestamps, and ingestion pipelines helps maintain accurate and trustworthy visualisations.
Configure role-based access
Different users require different levels of visibility.
Kibana supports role-based access control, allowing organisations to restrict dashboards, visualisations, and data according to user responsibilities while helping protect sensitive information.
Review and improve continuously
Dashboards should evolve alongside the business.
Regularly reviewing usage patterns, collecting user feedback, and updating visualisations ensures dashboards remain relevant as new requirements, systems, and data sources are introduced.
Following these practices helps organisations create dashboards that are easier to maintain, easier to interpret, and better aligned with business objectives.
Related article: Elastic Stack: How to integrate Elasticsearch, Logstash, and Kibana?
Why choose Kibana with Elasticsearch?
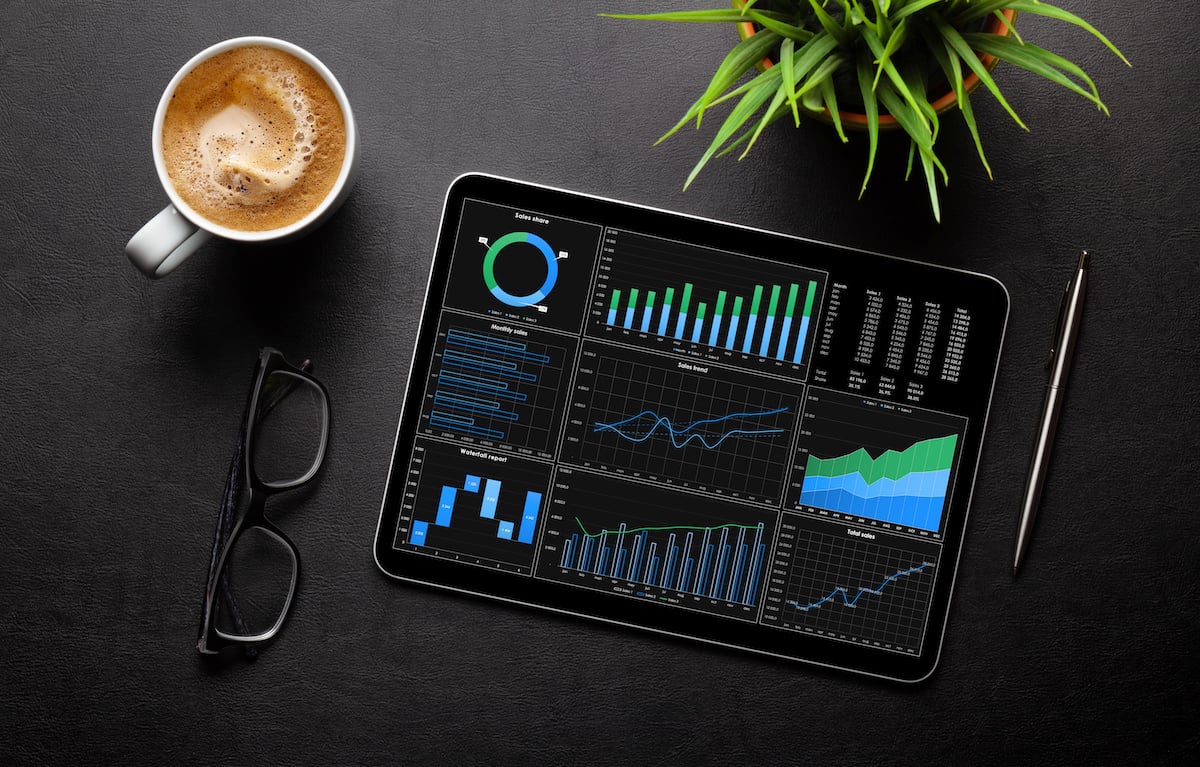
Kibana delivers its greatest value when combined with Elasticsearch.
Together, they provide an integrated platform for searching, analysing, visualising, and monitoring large volumes of data in near real time. Rather than relying on multiple disconnected tools, organisations can centralise operational, security, and business information within a single platform.
This integration supports a wide range of use cases, from observability and application performance monitoring to cybersecurity, log analysis, and business intelligence.
For organisations investing in the Elastic Stack, Kibana is more than a dashboarding tool. It is the interface that transforms raw data into meaningful insights, helping teams respond faster to incidents, improve operational visibility, and make more informed decisions.
Kibana has become an essential component of the Elastic Stack, enabling organisations to transform large volumes of data into actionable insights through intuitive dashboards and visualisations.
Whether the objective is monitoring infrastructure, analysing application performance, strengthening security operations, or tracking business KPIs, Kibana provides the visibility needed to make faster and more informed decisions.
The real value of Kibana, however, lies not only in its visualisation capabilities but in how it works alongside Elasticsearch to create a unified platform for search, analytics, and observability. By combining powerful data indexing with flexible dashboards, organisations can reduce complexity, improve operational efficiency, and gain deeper insights across their technology landscape.
At Syone, we help organisations design, implement, and optimise Elastic solutions that support observability, search, security, and data analytics initiatives. From deploying Elasticsearch and Kibana to building scalable monitoring platforms, our specialists help organisations maximise the value of their data.
Discover how Syone's Elastic services can help you build smarter dashboards and gain real-time visibility across your organisation.
Want to see how Elasticsearch turns your data into dashboards? Download our Elasticsearch datasheet.